LoginSchedule demoLoginSchedule demo
Employees hit a third-party consent screen at the moment of maximum momentum and stop. Trust objections are timing problems: answer them before the screen appears.
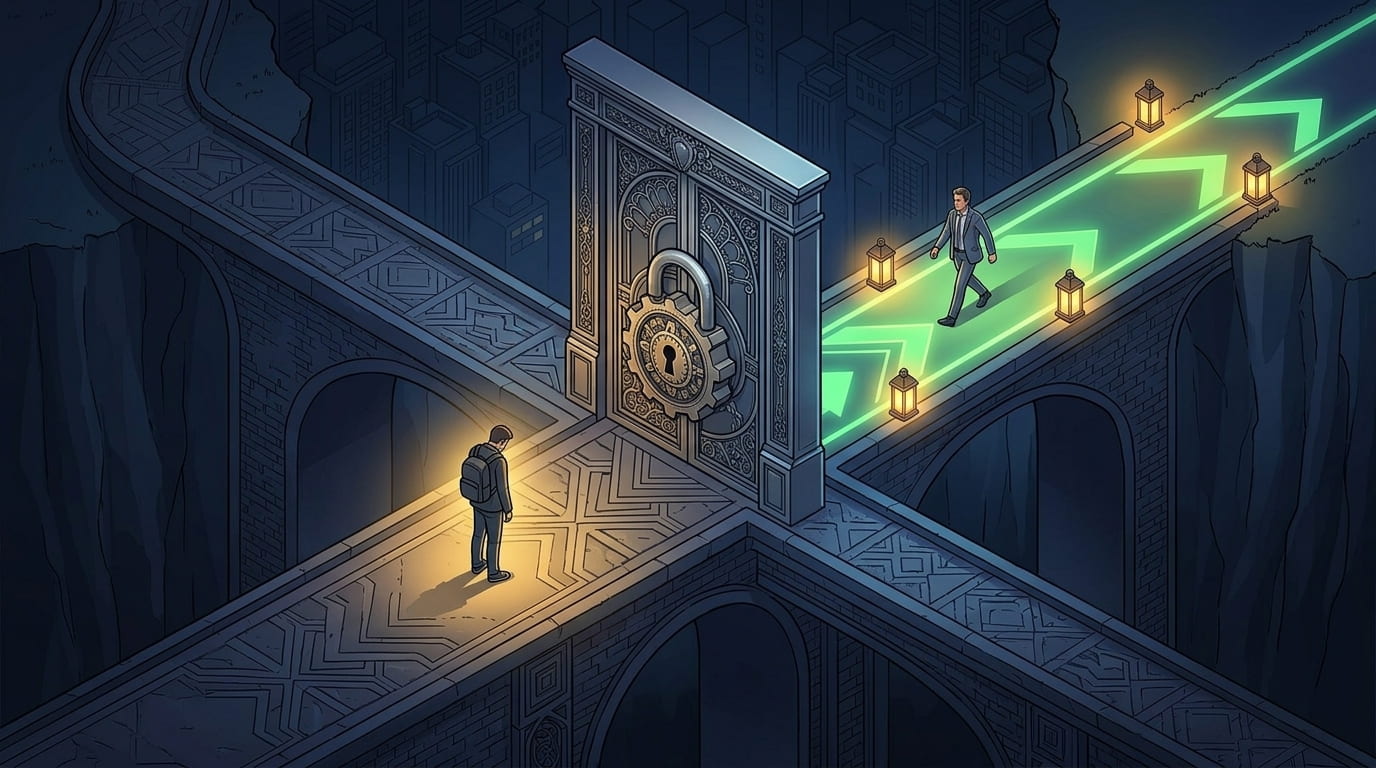
You can do everything right. Executive announcement out the week before. Content loaded into every group. IT allowlisting confirmed. Champions briefed. Launch email lands, people click, activation starts climbing, and then a chunk of your best advocates hit a wall roughly ninety seconds into signup.
The wall is a permissions screen. You didn’t write it. You have never seen it in your own admin console. And it does more damage to advocacy rollouts than any product limitation I have run into.
The single most expensive sentence in employee advocacy is a line of LinkedIn’s standard consent copy that says an app would like to create, modify, and delete posts on your behalf.
Read with context, it is unremarkable. Read cold, at 9:15 on a Tuesday by someone who was mildly curious about the program forty seconds ago, it says: my employer is about to get the keys to my LinkedIn account.
That person does not file a ticket. They close the tab.
Every rollout has a peak. It is the fifteen minutes after someone decides to try the thing. All your comms work is spent buying that window.
The consent screen sits exactly inside it. The employee has already given you the hardest yes, which is attention, and now they are asked for a second yes with unfamiliar legal-sounding language and no one in the room to interpret it. There is no colleague to lean over to. There is no FAQ open in the next tab. There is just a long list of permissions and a Cancel button that feels like the safe choice.
I watched this play out at one financial services rollout. The program team had done the work. The concern surfaced mid signup week, an employee flagged the wording, it moved through a couple of internal channels, and within two days the admin was fielding the same question repeatedly instead of celebrating activation numbers. The answer was straightforward. The answer was also arriving two days after the moment it needed to exist.
The information was fine. The timing was wrong.
Two things to understand before you write a word of comms about it.
First, the language belongs to LinkedIn, not to you and not to your vendor. LinkedIn defines the full menu of permissions any third-party application can request, and it defines how those permissions are described. Every tool your employees connect gets described in the same standardized phrasing. Nobody chooses friendlier wording, because friendlier wording is not on offer.
Second, and this is the reframe that does the most work: when the screen says an application would like to do something on your behalf, the requesting party is the application, not your admin team. The employee is granting the software permission to take actions they themselves trigger inside the product. They are not granting the communications department a window into their personal LinkedIn account. Almost every panicked reaction I have seen collapses the moment somebody says that plainly.
There is a third thing you should be honest about rather than tidy away. OAuth permissions are requested as a superset. An integration asks for the full set of scopes it needs across every feature it offers, not the narrow slice a given employee will use this week. So the list an employee reads is genuinely longer than their day-to-day experience of the tool. If you pretend otherwise, the first person who reads carefully will catch you, and then you have a credibility problem instead of a comms problem.
The specific strings and the length of the list change as LinkedIn revises its platform, so treat anything you write, including this post, as accurate as of 2026 and worth re-checking against the live screen before each launch.
Keep it short and put it in front of them before they see the screen, not after.
Tell them the screen is coming, and that it is long. Surprise is most of the damage. An employee who was told to expect a wall of permissions reads it as a step. An employee who was not reads it as a red flag.
Tell them who is asking. The application is requesting access so it can post the thing they chose to post. Their employer is not being handed an account.
Tell them plainly what is not reachable, because that is the list they actually care about. Not their direct messages. Not their browsing or who they looked up. Not their job search behavior or whether they have been talking to recruiters. Not the posts they write on LinkedIn outside the tool. And not their password, because the sign-in itself happens on LinkedIn’s own screen, which is the point of the design: the application is granted a scoped token instead of ever handling your password.
Give them something familiar to compare it to. Almost everyone reading has signed into an app with their Google account, or clicked Apply with LinkedIn on a job posting, or connected a social account to a scheduling tool. Same pattern, same kind of screen, same revocable connection. Naming that does more than three paragraphs of reassurance, because it converts an unfamiliar decision into one they have already made a dozen times.
And tell them they can revoke it whenever they want, from LinkedIn’s own settings, without asking anyone. People accept permissions far more readily when leaving is obviously easy.
That is five short things. It fits in a paragraph of the launch email and a slide in the training session. It does not need a policy document.
Finance, healthcare, legal, government. If that is you, this cannot live in a launch email. It belongs in onboarding, weeks ahead, in the conversation where you and your compliance stakeholders are already talking about what the program does with data.
The reason is not that your employees are more suspicious. It is that in these environments a single unanswered question can escalate into a review, and a review can eat a launch window. Surfacing the permissions screen early converts it from a discovered risk into an expected milestone. Your admin gets language they can use in one-on-ones and lunch-and-learns. Your compliance partner gets to ask their questions when there is time to answer them properly rather than during signup week.
A concern raised in onboarding is a conversation. The same concern raised mid-launch is an incident.
This is not really a post about OAuth.
Every rollout has trust objections waiting in it. Can my manager see what I share. Does this count against me if I don’t participate. Is this going to make me look like a corporate mouthpiece. What happens to this data. The permissions screen is just the one with a hard deadline attached, because it appears at a fixed point in the flow and it appears to everybody.
Trust objections are timing problems, not content problems. The answer barely changes depending on when you deliver it. The effect changes completely.
Answer it proactively and you have demonstrated that you understand your employees’ concerns before they voiced them, which is roughly the definition of earning trust. Answer it reactively and you have confirmed there was something to worry about, because you only brought it up once you were asked.
Same information. Opposite outcome.
So go look at your launch sequence and find the moments where an employee is asked to do something that might feel uncomfortable. Then move the explanation to just before each one. That is most of change management, and it costs you a paragraph.
Planning a launch? Our implementation team will walk your comms sequence with you and flag the friction points before your employees find them. Talk to our implementation team and we will start with this screen.
See the platform that comms, marketing, and compliance teams use to run their advocacy program.